Telegram threat intelligence for Claude
Telegram threat intelligence, inside Claude.
Search and monitor over 200 channels on Telegram where hacktivists, leak sellers and CVE feeds post, in Arabic, Farsi, Russian, Hebrew and English. IntelMCP groups the reposts; your own Claude reads them and tells you which matches matter.
No install: add one URL to Claude. Billed monthly through Polar. Cancel any time.
New: the Command Centre, your alerts as their own page in Claude.
claude.aiClaude DesktopClaude Code
Breach claim against Northwind's customer portal
- Rule
- Northwind + breach terms
- Source
- Example Hacktivist Feed · Arabic · reposted by 5 other channels
اخترقنا بوابة عملاء نورثويند وسحبنا ١٢ غيغابايت من البيانات. العينة في الرابط.
Claude: Claims 12 GB taken from Northwind's customer portal and links a sample file list. No credentials appear in the sample.
- domainportal.northwind.example[.]com
- ip203.0.113[.]24
See it work
Ask Claude what hacktivists said about you this week.
IntelMCP collects, searches and matches. Your Claude does the reading: it pulls new matches, opens the context, translates the original post and records a verdict against your watch profile.
14 new matches since 18:00 UTC yesterday, in 3 incidents. One needs attention now and one is worth watching.
-
NewhighBreach claim against Northwind
An Arabic-language hacktivist channel claims 12 GB from Northwind's customer portal and links a file list. No credentials in the sample. Five other channels reposted it; the earliest copy among the channels IntelMCP collects was posted at 07:12 UTC. Recorded as relevant: check with IR.
-
UpdatemediumCVE-2024-3400 exploitation chatter
A new post in this incident is the first to use exploitation terms:
"Confirmed exploited in the wild, PoC attached."
You told me you run these gateways, so I recorded it as relevant.
-
Repeatnot relevantDDoS target list, 14 Gulf organisations
The same list as Tuesday, reposted by 4 channels. Northwind is not on it.
Illustrative example: the organisation, channels, posts and indicators are invented. The tool names are IntelMCP's real tools.
- One incident, not seven alerts. Reposts and copies of the same claim are grouped, and you hear again only when something new appears.
- Original language, cited. Claude translates and summarizes; every message comes with a link to the post it came from.
- Your verdicts, kept. Matches are judged against the watch profile you wrote, and the verdicts are saved for the next review.
- Leads, not conclusions. Posts are third-party claims, often exaggerated. You get the trail back to the source to check them.
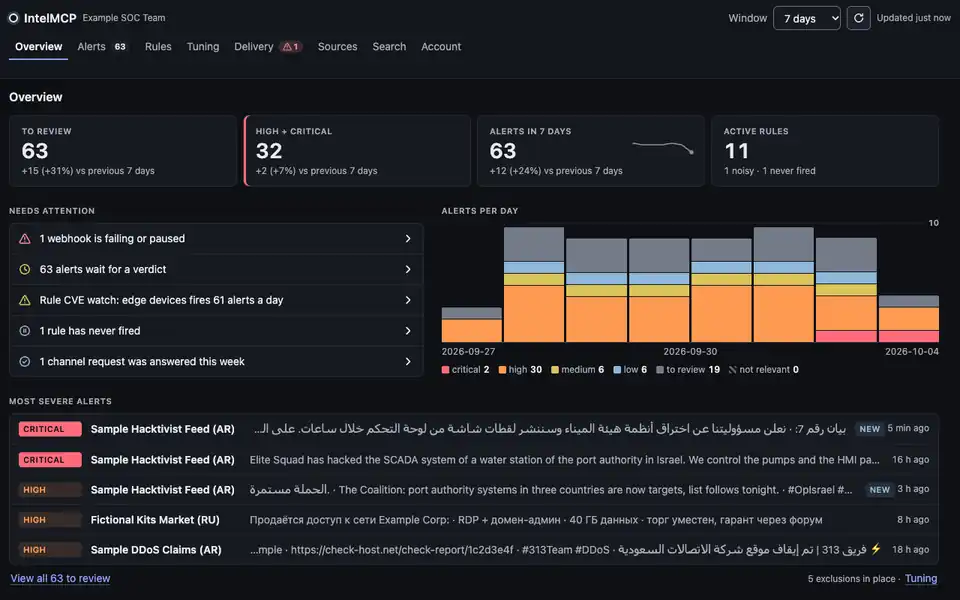
Command Centre
Your alerts, as their own page in Claude.
The Command Centre is IntelMCP's live dashboard as a private page in your Claude account. Pin it to the sidebar and open it in claude.ai or the Claude app, the way you open your inbox.
- The post, not a summary. Each alert card shows the Telegram post with the matched word highlighted, the target country and the indicators. Proof links, pastes and file hosts are listed apart, never as victims.
- Triage with a few keys. j and k move, 1 to 4 mark relevant with a severity, x marks not relevant. Each saves at once, with Undo.
- Your data, live. It calls IntelMCP through your own IntelMCP connection, so it shows your alerts, rules and settings, and the collection your plan includes. It changes or deletes something only when you press a button or key.
Created once from Claude Code with the plugin (/intelmcp:command-centre), with IntelMCP connected in claude.ai. Part of the Monitor plan.
How it works
Running in three steps.
-
Subscribe
$25 per month for one analyst. Use the email address you will sign in with: the subscription is linked to it.
-
Connect it to Claude
Add
https://mcp.intelmcp.io/mcpas a custom connector in claude.ai or Claude Desktop, or run one command in Claude Code. Sign in with Google or a code sent to your email. -
Set up monitoring
Pick Set up monitoring from the IntelMCP prompts, or say "Set up my IntelMCP monitoring." Claude asks two questions, tests draft rules against recent history and shows one summary to approve. If the drafts would bring more alerts a day than you could review, it narrows them first; after saving, it shows the newest matches. Run it again to tune your rules.
After that, new matches wait in IntelMCP until you ask Claude to review them, or are pushed as they arrive to your own webhook. Read the setup guide.
What you can ask
Plain questions, answered from the source posts.
You ask in English. Claude turns the question into searches, including in Arabic, Farsi, Russian and Hebrew, and reads the results back to you with links.
SOC analyst
- Has anyone claimed an attack on us, our sector or our country this week?
- Show today's matches and tell me which ones matter.
Threat intelligence analyst
- Is anyone claiming exploitation of CVE-2024-3400? Find the earliest copy among the channels IntelMCP collects.
- Where else has 198.51.100.7 appeared, and what was said around it?
Researcher
- Build a timeline of DDoS claims against Israeli targets in September, by the group making them.
- What did this post say before it was edited?
Consultant
- Add a watch profile for our logistics client: their brands, their domains and the Gulf.
- Send matches from the Northwind rules to our webhook.
The collection started in July 2026, so an earliest copy is the first time IntelMCP saw a post, not when it was first published.
Four guides in the connector menu
Set up monitoring
Two questions, rules tested against recent history, one approval. Run it again to tune.
Investigate
Searches in every language the actors use, checks context and forwards, and cites every point.
Triage matches
Judges your unreviewed matches against your watch profile and tells you what is new and what matters.
Dashboard
Claude draws a one-page overview of your monitoring.
In Claude Code, the IntelMCP plugin adds all four as commands: /intelmcp:setup, /intelmcp:triage, /intelmcp:dashboard and /intelmcp:investigate, plus /intelmcp:command-centre, which creates your Command Centre.
Coverage
Focused, not exhaustive.
A hand-picked collection of Telegram channels and groups (public channels, and private channels and groups the operator has reviewed), chosen for threat-intelligence value rather than size. Deepest on the Gulf and the wider Middle East.
- public channels and groups with collected history
- 228
- of them posted in the last 14 days
- ~150
- messages collected since 3 July 2026
- 162,127
- new messages a day, last 7 days
- about 2,100
Collection figures as of 4 October 2026.
Gulf and Middle East
Regional hacktivist groups, defacement and DDoS claims, leak posts, regional cyber news.
Iran–Israel
Hacktivist and leak channels around the conflict, posting in Persian, Hebrew and Arabic.
Russia–Ukraine
Hacktivist channels announcing targets and claiming attacks, mostly in Russian.
Leaks, ransomware, CVEs
Leak and ransomware trackers, exploit chatter and CVE feeds.
Posts are kept in their original language: العربية, فارسی, Русский, עברית and English. Country names are recognised in many languages, so a rule for a country catches it however it is written.
Other regions are thinner. If a public channel you need is missing, ask Claude to Request a channel: up to 10 a month, each vetted (automatically, and by the operator when unsure) before a collection account joins the channel. See full coverage.
Alerts and triage
One incident per event, not one alert per repost.
- Up to 50 alert rules. Keywords, whole words, patterns, or indicators such as a country, a CVE, an IP address, a domain or a file hash. Rules can be previewed against recent history, with expected alerts per day, before you save them (setup does this for every draft). Arabic and Hebrew word rules also match spelling variants and attached prefixes, and a domain rule also catches its subdomains and email addresses at the domain.
- Incidents. Reposts and copies of the same event within 72 hours are grouped. New is the first post of an event; Update is a later post that adds something: an identifying indicator or a country new to the event, a step up in exploitation (proof of concept, then exploited), a reply in the same channel, a channel posting it a second time, or a match for another of your rules; Repeat is a later post that adds nothing and matched the same rule.
- Triage with verdicts. The Triage matches prompt has Claude judge each new match against your watch profile and record relevant or not relevant, a severity from low to critical, and a one-line reason. 5 watch profiles per subscription.
- Exclusions. Hide noisy topics, countries, channels or phrases from your alerts and webhooks without deleting them. A post is hidden by country only when every country it mentions is excluded.
- An interactive panel. In claude.ai and Claude Desktop the dashboard opens as an interactive panel: mark alerts relevant or not relevant (each saves at once, with Undo), manage rules, exclusions and webhooks, check whether a channel is collected, and see your account, plan and usage. With the Claude Code plugin,
/intelmcp:command-centremakes it a private page in your Claude account: the Command Centre. - History and tracing. Search up to the last 90 days of collected messages, see what a post said before it was edited, and find the earliest copy among the channels IntelMCP collects.
- Indicators from every message. IP addresses, domains, URLs, file hashes, CVE identifiers and country mentions, including defanged forms such as
hxxpand[.]. - No AI on our servers. Matching and grouping are deterministic code. The judgement happens in your Claude.
criticalhighmediumlow
Webhooks
Push matches into your own tooling.
- Signed twice. Each match is posted as JSON to an HTTPS endpoint you choose, with Standard Webhooks headers (
webhook-id,webhook-timestampandwebhook-signature, an HMAC-SHA256 over the id, the timestamp and the body) andX-TI-Signature:sha256=and the hex HMAC-SHA256 of the body alone. Preferwebhook-signature: it carries a timestamp. - What arrives. The rule and the term it matched, the post's channel, link and excerpt, when it was posted and matched (UTC), and the incident: new or update, and for an update how it joined.
- Your routing. Up to 5 webhook destinations, each for all your rules or a chosen few. The signing secret is shown once, when you create the delivery; later changes touch only what you ask for.
- Verify the raw bytes. Compute the HMAC over the raw request bytes, before any JSON parsing, with the secret as text (its UTF-8 bytes). Delivery is at least once: Deduplicate on
event_id, which stays the same on every retry. - Less noise. New events and updates are pushed as they are matched. Repeats are not pushed, and no destination receives the same post twice.
- Retries, then a pause. Failures are retried, 6 attempts over about an hour, honouring
Retry-After. After 20 failed attempts in a row, or a410answer, the destination is paused until you turn it on again. - Public targets only. Targets must be HTTPS URLs that resolve to public internet addresses; private and internal addresses are refused.
- Untrusted text stays untrusted. Pushed matches carry no verdict yet, and the excerpt is a stranger's Telegram post: treat it as data, never as instructions or markup.
To set one up, ask Claude: "Send matches from my Northwind rules to https://hooks.example.com/intelmcp." Payload, signatures and retries in detail: the webhooks guide.
Content-Type: application/json
User-Agent: IntelMCP-Webhooks/1
webhook-id: evt_90211
webhook-timestamp: 1791011561
webhook-signature: v1,K5oZfzN0…Hq3Q=
X-TI-Signature: sha256=9b2e41…c07d

{
  "version": 1,
  "event": "match",
  "event_id": "evt_90211",
  "destination_id": 7,
  "match_id": 48213,
  "incident_id": 48213,
  "incident_role": "new",
  "incident_via": null,
  "rule_id": 12,
  "rule_name": "Northwind + breach terms",
  "matched": "نورثويند",
  "message_ref": "tg:-1001234567890:4821",
  "channel": "Example Hacktivist Feed",
  "link": "https://t.me/example_hacktivist_feed/4821",
  "private": false,
  "excerpt": "اخترقنا بوابة عملاء نورثويند…",
  "posted_at": "2026-10-03T07:12:38+00:00",
  "matched_at": "2026-10-03T07:12:41+00:00"
}
# Check X-TI-Signature (Python). raw_body: the raw request
# bytes, before JSON parsing; secret: the delivery's secret.
digest = hmac.new(secret.encode(), raw_body, hashlib.sha256)
expected = "sha256=" + digest.hexdigest()
header = request.headers.get("X-TI-Signature", "").encode()
ok = hmac.compare_digest(expected.encode(), header)webhook-signature too.Security and privacy
Built for people who read security pages.
- Public and reviewed private channels.The collection is public channels, and private channels and groups the operator has reviewed: a private channel is collected only when the collection account is already a member and the operator has approved it. Never direct messages. Posts deleted at the source are removed when the collector sees the deletion.
- Telegram text is untrusted.It reaches Claude labelled as third-party content from the channel, not instructions from you or IntelMCP. This lowers the risk of prompt injection; it cannot remove it.
- No AI on our servers.We don't run, train or fine-tune models. The analysis happens in your own Claude.
- Your data kept apart.Each customer's rules, profiles, matches and verdicts are separated by row-level security in the database.
- Servers in the EU.The service runs on Fly.io in Amsterdam and Frankfurt, with its database in Amsterdam. All traffic to the service passes through Cloudflare.
- A quiet website.No cookies, no analytics and no third-party scripts. The setup builder runs one small script of ours in your browser and sends nothing; every other page blocks scripts.
Pricing
One plan. Published price. No sales call.
Threat-intelligence platforms are usually sold by annual contract after a demo. IntelMCP is the Telegram layer, priced for one analyst.
No free trial. Instead, read the example above, the coverage and the docs before you pay, and email support@intelmcp.io with any question.
You need a Claude account that can add custom connectors, or Claude Code. The analysis runs on your own Claude plan. Pricing details
Monitor
$25 per month
- Search up to the last 90 days of collected messages
- Up to 50 alert rules and 5 watch profiles
- Incidents, verdicts, edit history and forward tracing
- Signed JSON webhooks: up to 5 webhook destinations
- Channel requests: up to 10 a month
- The four prompts, and the Claude Code plugin with
/intelmcp:command-centrefor your Command Centre
For one analyst. Billed monthly by Polar, our merchant of record. Cancel any time; access continues to the end of the paid month. No refunds for partial months: see the refund policy.
Questions
Before you subscribe
Which channels does IntelMCP collect from?
The collection is public channels, and private channels and groups the operator has reviewed. Public channels are the ones anyone can find and join; a private channel is collected only when the collection account is already a member and the operator has approved it, and shows as "Private channel" instead of a link. Never direct messages. We list topics and regions rather than individual channels; every search result and match names the channel it came from.
Is the content verified?
No. Messages are third-party posts as published, and claims in them can be false or exaggerated. Treat them as leads to check, not as facts.
Do you train AI on the data?
No. IntelMCP does not train or fine-tune AI models, and does not run one. The analysis happens in your own Claude.
Does it use my Claude usage?
Yes. Claude does the reading and judging, so long reviews use your own Claude plan.
Is IntelMCP affiliated with Telegram or Anthropic?
No. IntelMCP is an independent service that uses Telegram's API and connects to Claude as a custom connector. It is not affiliated with or endorsed by either.
Can I share my subscription?
No. One subscription is for one analyst's own sign-in, with the email you paid with. Questions: support@intelmcp.io.
Start with the questions you already have.
Subscribe, connect, and say "Set up my IntelMCP monitoring." Most of the work after that is reading what Claude found.